


Amazon Bedrock
Integration
Your company deploys AI agents faster than it can secure them.
Unosecur brings them into one control plane to trace access, detect drift, and remove standing privileges.
Close the security gaps behind Bedrock agents.
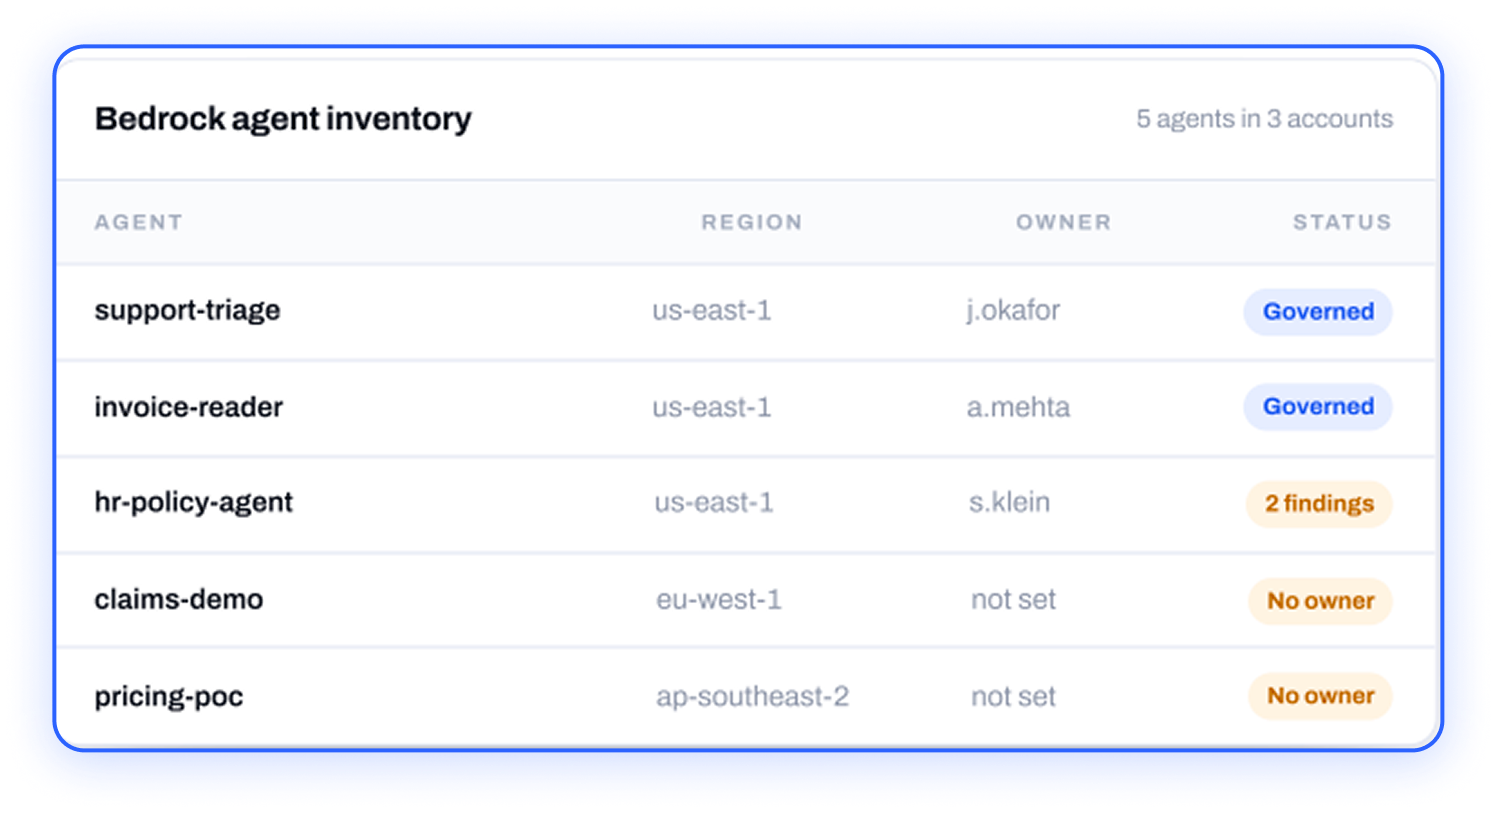
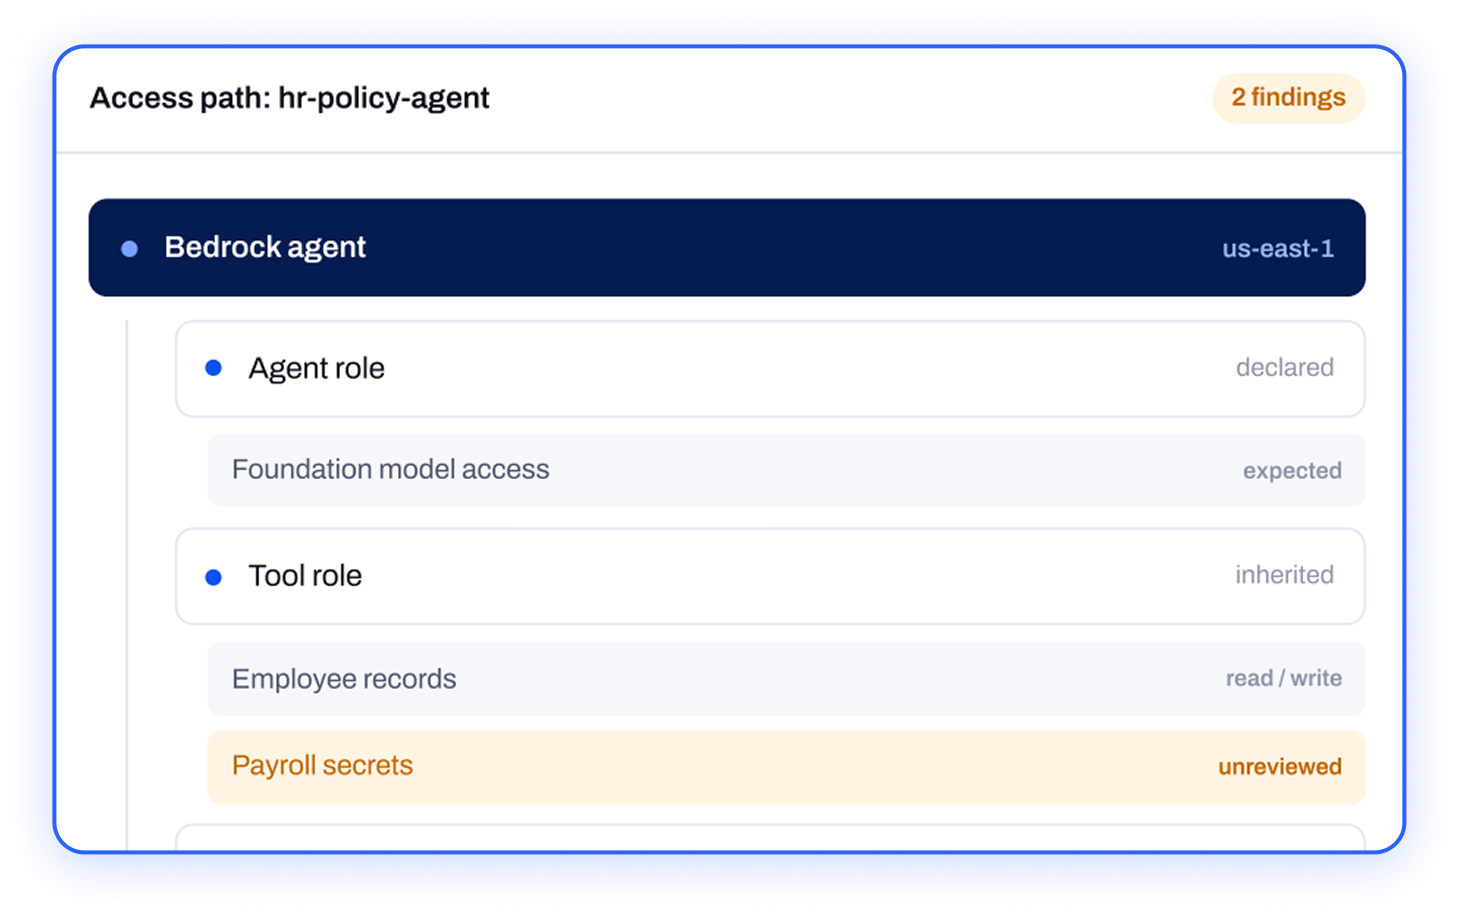
The agent visible in AWS is only the starting point. Ownership, guardrails, inherited privilege, connected data, and activity determine the risks security teams must contain.
Turn Bedrock visibility into security control.
Connect a single AWS account to discover, prioritise and reduce agent risk. No workloads go offline, and development keeps moving.
VISIBILITY
Find every AI agent
Inventory agents, owners, guardrails, tools, and data sources across accounts and Regions.
RISK
Prioritise dangerous exposure
Rank excessive privilege, escalation paths, credentials, and behaviour by the systems and data at risk.
CONTROL
Reduce standing privilege
Right-size policies, enforce just enough privilege, and route remediation to the owner.
AI agent exposures living in your AWS accounts today.
Standard cloud security tools scan static infrastructure. They completely miss the application layer context of generative AI.
Orphaned AI access
The owner leaves, but the agent's service role and permissions can remain active. Human offboarding does not automatically retire the agent's access.
Unmonitored agent sprawl
Bedrock agents are regional resources. Agents can spread across accounts and Regions, making active and privileged deployments easy to miss.
Hidden tool permissions
Action groups can invoke Lambda functions and APIs through the agent's configured permissions. Reviewing the agent alone can miss the downstream access those actions inherit.
Unbounded knowledge access
A knowledge base can expose more content than the agent's intended task requires. The effective boundary depends on the data source, retrieval configuration, and permissions behind it.
Broken user-to-agent attribution
Agent actions execute through service identities, which can separate the downstream action from the human who initiated it. Investigation requires linking user, session, agent, and role activity.
Missing invocation evidence
Bedrock model invocation logging is disabled by default and configured per Region. Without it, investigations can lack request and response context for supported model calls.
Integrations
One fabric across every AI platform below
Unosecur bridges cloud providers, identity platforms, and SaaS applications to bring agent behavior and authority into one strategic view.