


Microsoft Copilot Studio
Integration
Your company deploys AI agents faster than it can secure them.
Unosecur brings them into one control plane to trace access, detect drift, and remove standing privileges.
Close the security gaps behind Copilot Studio agents.
The agent visible in Copilot Studio is only the starting point. Ownership, agent identity, authentication, connectors, tools, knowledge sources, and activity determine the risks security teams must contain.
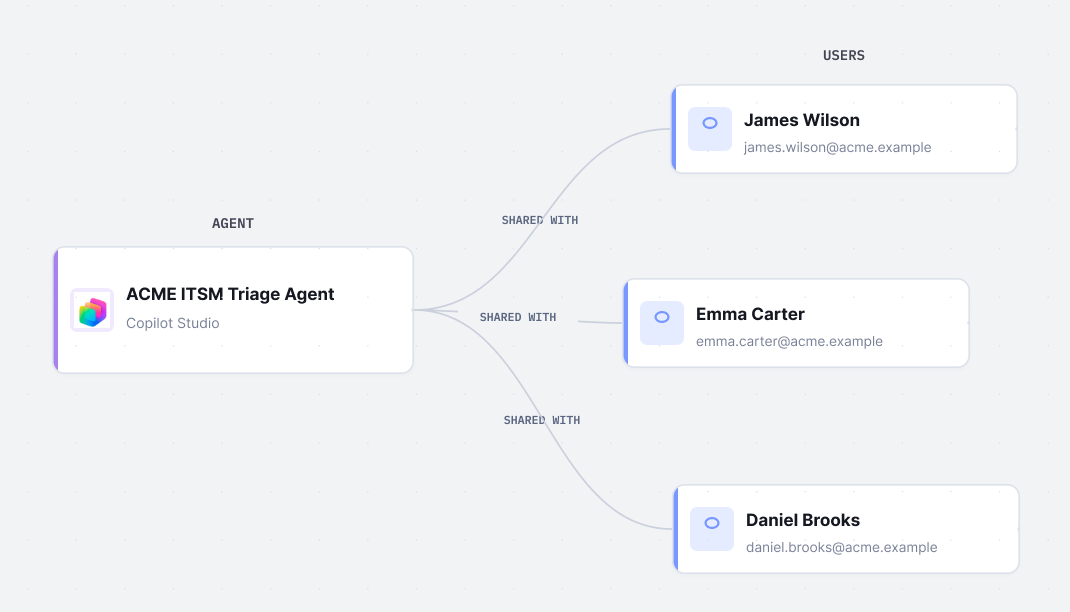
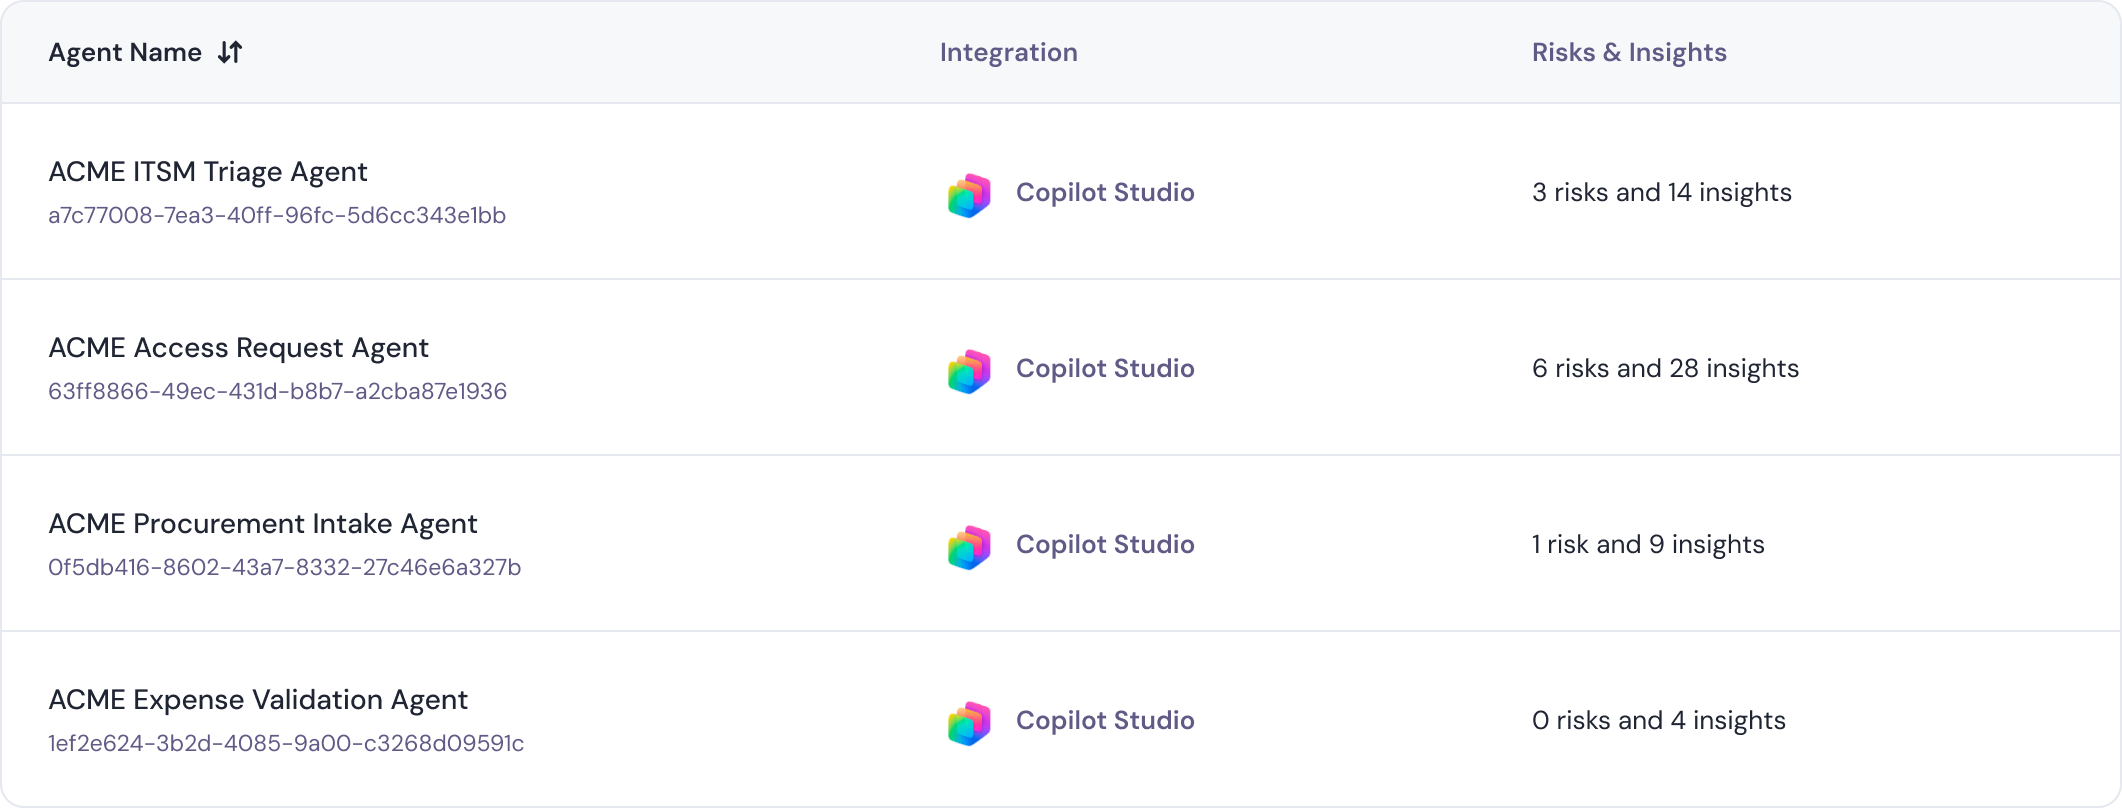
AI agent exposures living in your Copilot Studio environments today.
Existing SaaS and identity controls show users and permissions. They do not by themselves explain how agent ownership, tools, connections, and downstream access combine into risk.
Everyone is a builder
Every licensed user is a maker in the default environment. Agents touch production data without ever passing a review, an environment boundary, or a DLP policy.
Agents run as the builder
Connections are shared with the agent, not scoped to the user. Every employee who opens it is operating at the builder's permission level.
Published with no sign-in
An agent can be published to a website with authentication set to none. Anyone with the link reaches whatever the agent reaches, with no identity attached.
Policies applied too late
Agents built before a DLP policy existed keep the connections they were born with. Data moves from an internal system to an external one with nothing stopping it.
Whole sites as knowledge
Makers point agents at entire SharePoint sites instead of specific libraries. The agent returns anything in scope, including what the person asking should never see.
The maker leaves, the agent stays
The maker is offboarded. The agent stays published and keeps running on the stored connection. Nobody is accountable for it anymore.
Integrations
One fabric across every AI platform below
Unosecur bridges cloud providers, identity platforms, and SaaS applications to bring agent behavior and authority into one strategic view.
Deploy AI agents fast. Secure them faster.
Discover every agent. Prioritize riskiest access. Reduce standing privileges.